The Shopify “Backdoor” Mystery: How Bots Bypass Cloudflare and How to Stop Them
TL;DR:
Many Shopify merchants are suffering from relentless bot attacks despite having Cloudflare and premium security apps. The “mystery” was recently solved: bots are bypassing custom domains entirely and hitting the internal myshopify.com subdomain, which is hard-routed through Shopify’s own Enterprise Cloudflare. The only definitive fix discovered is enforcing Customer Accounts Required for Checkout.
Recently, our team at DiscoverMyBusiness helped a client uncover a massive blind spot in Shopify’s architecture that was allowing malicious traffic to bypass standard security layers. This discovery is a core part of our
Table of Contents
- The Anatomy of a Modern Bot Attack
- The Discovery: The myshopify.com Vulnerability
- Why This Is a “Blind Spot” for Shopify
- The Solution: “Forcing the Handshake”
- Implementation Guide: Securing Your Store
- The Trade-Off: Conversion vs. Security
- Frequently Asked Questions (FAQ)
- Summary Table: Comparing Defensive Strategies
- Partner with DiscoverMyBusiness
The Anatomy of a Modern Bot Attack
In the late 2024 and early 2025 landscape, the nature of bot traffic shifted from simple data harvesting to aggressive transactional interference. For Shopify merchants, this isn’t just a nuisance; it’s a direct threat to operational integrity and merchant standing with payment processors. This shift mirrors the changes we discuss in our
The Shift: From Scrapers to “Ghost Shoppers”
Historically, bots were used to scrape prices or steal content. The modern bot attack, like the one recently uncovered, is different. These are “Ghost Shoppers” that target the checkout flow.
Key Characteristics of the 2025 Bot Wave:
- High-Volume Cart Creation: Bots add items to carts at a rate of hundreds per minute, locking up inventory if your site has “cart-reserve” logic.
- Abandoned Checkout Bloat: Your Shopify “Abandoned Checkouts” dashboard becomes flooded with thousands of fake entries, making it impossible to run automated
Email Marketing Services - “John Doe” Profile Generation: Thousands of fake customer profiles are created, often using scrambled emails or common names like “John Doe,” which clutters your CRM and skews your Customer Lifetime Value (CLV) data.
- Payment Gateway Probing: Often, these bots are testing stolen credit card lists. Even if the transaction fails, your payment gateway (Shopify Payments, Stripe, etc.) sees a massive spike in “declined” attempts, which can lead to your account being flagged or suspended.
Why the “Gold Standard” of Security is Failing
Most high-revenue Shopify merchants utilize a “Layered Defense” strategy. On paper, this should be impenetrable. However, the mystery discovered by the community proves that these layers have a fundamental flaw: they assume the bot is coming through the front door. This is why a comprehensive
A. The Limitation of Custom Cloudflare WAF Rules
Web Application Firewalls (WAF) are brilliant for blocking traffic based on:
- ASNs: Blocking known data centers like AWS or DigitalOcean.
- Geofencing: Blocking countries where you don’t do business.
- Rate Limiting: Blocking any IP that hits “Add to Cart” more than 5 times in a minute.
The Failure Point: These rules only execute if the traffic passes through your DNS. As the Reddit community discovered, bots are now bypassing the custom domain (brand.com) entirely, meaning your WAF rules never even “see” the attack. This is a common issue we address in our
B. The Gap in Shopify Bot Protection Apps
Many merchants pay hundreds of dollars monthly for premium apps that use JavaScript to analyze user behavior (e.g., mouse movements, click patterns).
- The Logic: If it doesn’t move like a human, it’s a bot.
- The Failure Point: Sophisticated bots are now “headless.” They don’t load the JavaScript or the CSS of your storefront. They interact directly with the backend API. If the app relies on a script running in the browser, and the bot never opens a browser, the app is blind. This failure in user detection is why we prioritize
User Behavior Analytics
C. The “Captcha” Bypass
Implementation of hCaptcha or reCAPTCHA is often cited as the ultimate fix.
- The Logic: Force a “human test” before an item is added to the cart.
- The Failure Point: Bots are increasingly targeting the checkout.shopify.com or the direct subdomain endpoints. Since the “Add to Cart” button on your theme is just a visual trigger, bots can bypass the button (and its Captcha) and send a direct POST request to the server to create a checkout session.
The Technical “Smoking Gun”
The reason these layers fail simultaneously is documented in the server logs. Merchants found that while their Cloudflare dashboard showed “0 threats blocked,” their Shopify analytics showed “10,000 active sessions.”
Critical Insight: The traffic was reaching the checkout because it was routed through Shopify’s internal Enterprise Cloudflare network, not the merchant’s Pro/Business account. This “hard-routing” means the bots found a path that is effectively invisible to the merchant’s security stack. This highlights the importance of our
The Discovery: The myshopify.com Vulnerability
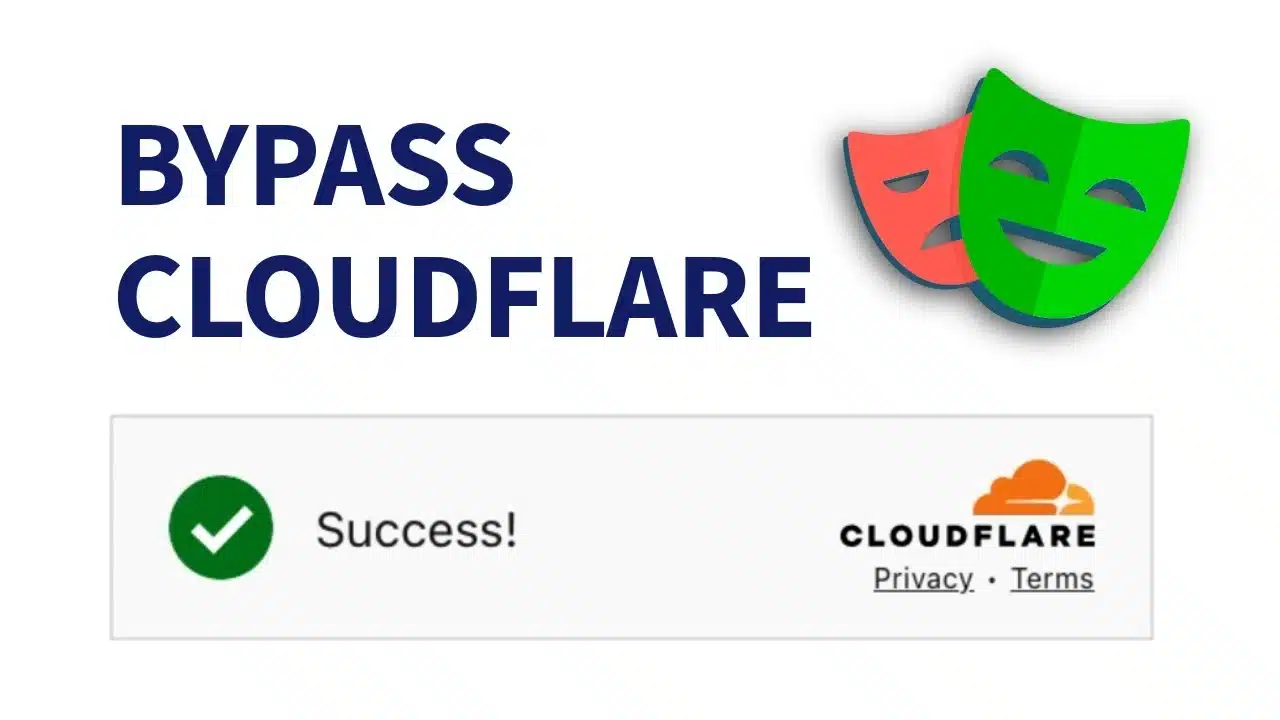
The “mystery” was finally solved when deep log analysis revealed a startling pattern: the bots were completely ignoring the primary domain. While merchants were busy hardening www.brandname.com, the attackers were sending high-velocity requests directly to brandname.myshopify.com.
The Subdomain Logic Gap
This discovery exposed a fundamental architectural “loophole” in how Shopify handles traffic. Because every Shopify store is built on a permanent .myshopify.com backbone, that URL remains active even after you connect a custom domain.
Why This is a “Backdoor”
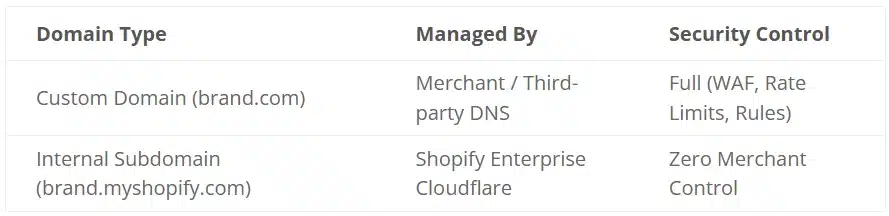
When you use a service like Cloudflare Pro or Business, you are essentially putting a security guard at your front door (brand.com). However, the brandname.myshopify.com subdomain acts as a side entrance that is hard-routed through Shopify’s own Enterprise Cloudflare layer.
The critical flaw? Your custom security rules do not propagate to Shopify’s Enterprise layer. To a bot, this is like finding an unlocked window. By targeting the internal subdomain, they “tunnel” under your defenses, rendering your expensive WAF rules, IP blocks, and custom rate limits completely invisible to the incoming traffic.
Technical Note: Even if you have “Traffic Proxying” enabled, the internal Shopify routing priorities often allow direct requests to the .myshopify endpoint to resolve without ever touching the merchant’s external DNS filters. To ensure your conversions are actually human, we recommend a secondary
Why This Is a “Blind Spot” for Shopify
When merchants discover the subdomain bypass and escalate the issue to Shopify Support, they are frequently met with a “dead end.” This isn’t necessarily due to a lack of effort from support staff, but rather a fundamental limitation of Shopify’s high-availability “Enterprise” architecture. This infrastructure challenge is a core reason why many brands seek an
The “Orange Cloud on Orange Cloud” Conflict
Most high-growth brands use Cloudflare to protect their site (indicated by the “Orange Cloud” icon in Cloudflare settings). However, Shopify itself is one of the world’s largest users of Cloudflare Enterprise.
- The Routing Layer: When you add your own Cloudflare layer, you are effectively placing your security rules on top of Shopify’s.
- The Bypass: Bots have learned that if they target the myshopify.com subdomain, they are interacting directly with Shopify’s Enterprise layer, completely jumping over the merchant’s specific Cloudflare instance.
- The Conflict: These two layers do not “talk” to each other. Your custom WAF rules exist only in your bucket, while the myshopify.com traffic stays in Shopify’s bucket.
The Infrastructure Response: “Shared Security”
When asked to block specific IPs or ASNs on the internal subdomain, Shopify’s standard response is that they cannot apply custom WAF rules to individual .myshopify.com URLs. This lack of control highlights the need for a resilient
The reasoning is twofold:
- Shared Infrastructure: The internal routing system is a shared environment. Applying granular, merchant-specific blocks at the platform level could theoretically interfere with the stability of other stores or Shopify’s core services.
- Platform Neutrality: Shopify’s automated bot protection is designed to be “always-on” and global. They rarely allow individual merchants to “tune” the backend firewall settings for a URL that Shopify considers a core system identifier.
The Result: A Security Limbo
The merchant is left in a vulnerable position. They are forced to maintain a URL (brand.myshopify.com) that:
- Cannot be deleted: It is the permanent database ID for the store.
- Cannot be “De-indexed” effectively: Even if hidden from Google, bots already have the URL.
- Cannot be protected: Your custom-paid security tools are rendered spectators while the attack continues through the “backdoor.”
The Reality Check: Because Shopify’s infrastructure prioritizes uptime and platform-wide stability, the burden of “solving” a targeted bot attack often falls entirely on the merchant’s ability to find creative workarounds within the admin settings. It may be time to
The Solution: “Forcing the Handshake”
After the Reddit community and various high-volume merchants tested dozens of “surface-level” fixes, such as hiding Out of Stock (OOS) products or blocking entire continents via ASN filters, only one solution emerged as a definitive “hard stop” for the subdomain bypass.
The “Required Account” Method
The most effective way to neutralize this attack is to move the barrier from the Network Layer (Cloudflare) to the Application Layer (Shopify’s internal logic). By navigating to Settings > Checkout and selecting “Require customers to log in to their account before checkout,” you fundamentally change the rules of engagement for every visitor.
How It Works: The Technical Logic
To understand why this stops bots that have already bypassed your firewall, you have to look at the “Handshake” process.
1. The Mandatory Auth Handshake
When guest checkout is enabled, the /checkout endpoint is “public-facing.” A bot can send a direct request to that URL and receive a session ID. However, when you require an account, Shopify’s backend logic initiates a mandatory authentication check before it even attempts to build a cart session.
2. Breaking the Bot’s “Direct Path”
Most checkout bots are built for speed and efficiency. They are programmed to hit the /cart/add or /checkout endpoints directly to bypass the slow process of loading a website’s theme.
- The Conflict: These bots are almost never equipped to handle a multi-step authentication flow, especially “New Customer Accounts” that require a one-time passcode (OTP) from an email.
- The Result: The bot hits the “wall” of the login screen. Since it cannot provide a verified customer token, the Shopify server refuses to generate a checkout session, effectively “starving” the bot of the data it needs to continue. This methodology is similar to how we use
Claude.ai Agent Setup
3. Closing the “Backdoor”
This is the most critical part: The login requirement applies to the .myshopify.com subdomain as well. Even though the bot found the “backdoor” URL to bypass your Cloudflare WAF, it cannot bypass Shopify’s internal requirement for a customer ID. By forcing a login, you are essentially telling the Shopify server: “Do not talk to anyone who hasn’t been verified by my primary authentication system.”
Expert Insight: This method works because it moves the defense to the one place the bot cannot bypass, Shopify’s own core database. If the database requires a customer_id to create a checkout_id, and the bot doesn’t have one, the attack ends right there.
Implementation Guide: Securing Your Store
To implement the “Mystery Solved” fix and close the subdomain loophole, follow these three tactical steps within your Shopify admin.
Step 1: Enable Mandatory Accounts
This is the “Kill Switch” for the current bot wave.
- Log in to your Shopify Admin.
- Navigate to Settings > Checkout.
- Scroll to the Customer Accounts section.
- Select “Require customers to log in to their account before checkout.”
Step 2: Transition to “New Customer Accounts”
While Shopify offers “Classic” and “New” account styles, the New Customer Accounts are superior for bot prevention.
The Logic: Classic accounts rely on passwords, which bots can attempt to brute-force or use from leaked databases (credential stuffing).
The Benefit: New Customer Accounts use a 6-digit One-Time Passcode (OTP) sent to the user’s email. This requires the bot to not only hit your site but also have real-time access to a unique email inbox, a barrier that stops 99% of automated scripts. This is much more secure than the
Step 3: Automated Cleanup with Shopify Flow
If you are on a Shopify plan that supports Shopify Flow, you can automate the “trash collection” of any bots that manage to create a profile.
- Trigger: Customer created.
- Condition: Check for common bot identifiers (e.g., First Name is “John” AND Last Name is “Doe” OR Email contains suspicious strings like mail.ru or temp-mail.org).
- Action: Delete customer or add a “Bot” tag for manual review.
Pro Tip: If you use a third-party marketing tool like Klaviyo, ensure your Flow excludes these bot-tagged profiles so you aren’t paying for “ghost” subscribers in your email list. This type of automation is a core part of our
The Trade-Off: Conversion vs. Security
In the world of e-commerce, friction is the enemy of conversion. Every additional click, field, or login screen you place between a customer and the “Buy” button carries a mathematical risk of cart abandonment.
The “Friction” Reality Check
Requiring a login adds a significant step to the checkout process. For a legitimate customer, this means:
- Stopping to check their email for an OTP (One-Time Passcode).
- Switching apps on their mobile device.
- Remembering which email address they want to use for the purchase.
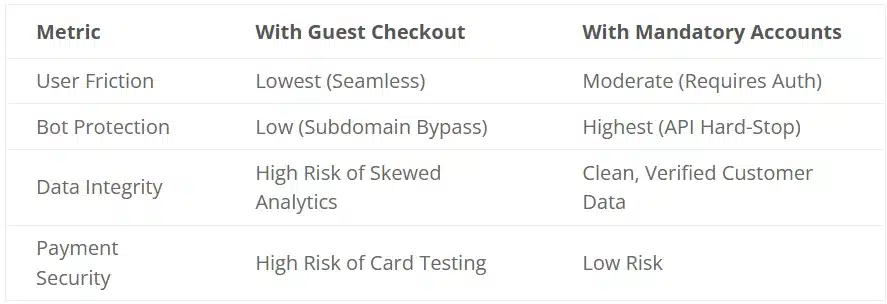
Data typically shows that mandatory accounts can lead to a 10% to 30% drop in conversion rates for first-time shoppers who value speed above all else. However, when your store is under a massive bot attack, the “cost” of not acting is often much higher than the cost of friction.
Our Recommendation: Tactical Hardening
We suggest viewing “Mandatory Accounts” not as a permanent branding choice, but as a tactical defensive maneuver.
- Phase 1: Immediate Defense: If you are currently seeing thousands of “John Doe” profiles or high-velocity checkout attempts, enable the feature immediately. It is better to lose a few legitimate sales than to have your payment gateway suspended or your inventory data corrupted by tens of thousands of bot sessions.
- Phase 2: The “Cool-Down” Period: Bot farms are run like businesses; they have limited resources. Once they realize your site is “hardened” and their scripts are failing, they will likely move on to an easier target.
- Phase 3: The Re-Entry Test: After the attack subsides (typically 7–14 days of zero bot activity), you can experiment with returning to Guest Checkout. Monitor your logs closely; if the bots return, you now have the “Kill Switch” ready to go.
Summary of the Trade-Off
Frequently Asked Questions (FAQ)
Can I just delete my .myshopify.com subdomain?
No. This is the permanent internal ID of your store. It cannot be deleted or changed after the store is created.
Will Shopify Plus Bot Protection fix this?
Shopify Plus offers “Bot Protection” features that can be scheduled for flash sales. While more powerful, even some Plus merchants have reported bypasses if the bots are sophisticated enough to target the backend API directly.
Does this affect my SEO?
No. Enforcing a login at checkout does not prevent Google or Bing from crawling your product pages or blog posts. It only protects the transaction layer.
Why doesn’t Shopify just let me put my own Cloudflare on the subdomain?
Shopify manages the .myshopify.com domain at an enterprise level to ensure platform stability. Allowing individual DNS control over these subdomains would create massive security and routing complexities for their core infrastructure.
Does “Required Accounts” break my Shop Pay or Apple Pay?
No. Standard accelerated checkouts like Shop Pay and Apple Pay still function, but the user must be authenticated. If they have a Shop Pay account, the “handshake” often happens automatically, reducing the friction. We offer
Can I block the .myshopify.com URL using a robots.txt file?
You can add a “disallow” rule to your robots.txt, but this only tells “good” bots (like Google) not to crawl it. Malicious bots completely ignore robots.txt instructions, so it will not stop an attack. This is why we focus on
Will this stop bots from scraping my product prices?
No. This fix specifically protects the checkout and customer creation flow. If bots are simply scraping your front-end content, you still need a robust WAF or a JavaScript-based challenge on your product pages.
How do I know if I am being targeted via the subdomain?
Check your server logs or Shopify “Sessions by Landing Page” report. If you see a massive spike in traffic where the “Host” or “Domain” is listed as your .myshopify.com URL rather than your primary domain, you are likely being targeted by this bypass.
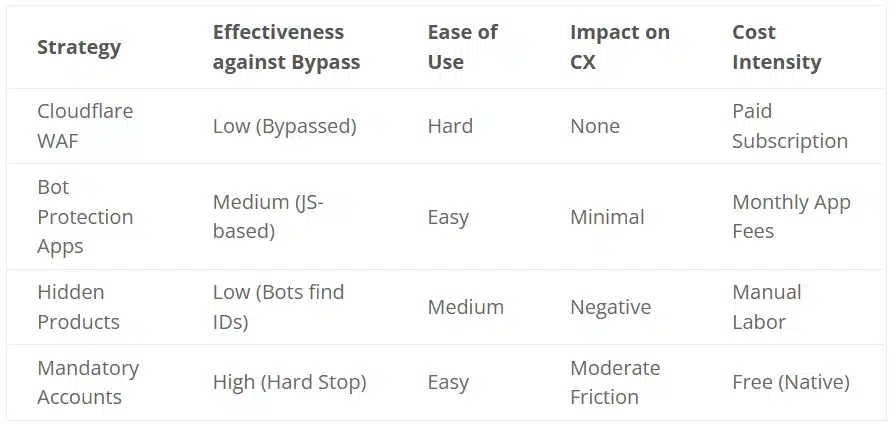
Summary Table: Comparing Defensive Strategies
This table provides a high-level comparison of the most common defensive measures used by Shopify merchants and how they stack up against the specific myshopify.com subdomain bypass.
Final Takeaway
While traditional SEO and security focus on the “Front Door” (your custom domain), the modern landscape requires you to secure the “Service Entrance” (the Shopify internal subdomain).
The discovery that Mandatory Customer Accounts serve as a definitive API-level firewall is a game-changer for merchants who have exhausted their budgets on external security tools. If your analytics are being sabotaged and your inventory is being held hostage by “Ghost Shoppers,” it is time to enable the login handshake and reclaim your store’s data integrity.
Partner with DiscoverMyBusiness
Technical vulnerabilities like the Shopify subdomain bypass require more than just standard digital marketing; they require a deep understanding of e-commerce architecture.
At DiscoverMyBusiness, we specialize in bridging the gap between high-performance marketing and technical security. Whether you’re scaling to seven figures or defending your store against malicious traffic, our team is here to ensure your growth is built on a secure foundation.
Contact us today to audit your Shopify security and content strategy.
(877) 522-7738
Blogs
Virtual Legal Staffing: How Tools Like Legal Soft Are Changing the Industry
Virtual legal staffing allows law firms to scale dedicated remote support at a fraction of the cost of traditional in-house hiring.
TextExpander: Pricing, Features, Snippets & Team Text Expansion
See TextExpander plans from free to Enterprise, plus Snippets, fill-ins, shared team libraries, and AI Recommendations, and learn if it is worth it for your team.
How to Fix Duplicate Product Schema in Shopify
Seeing multiple Product objects on your Shopify product page? Learn how to find duplicate Product schema, trace its source, fix it safely, and keep it from coming back.
PageFly: Pricing, Features, AI Page Builder & CRO for Shopify
See PageFly plans from free to Enterprise, plus FlyMate AI page building, heatmaps, A/B testing, and AI Page Checkup, and learn if it is worth it for your Shopify store.
What We Learned From Two Weeks of Talking to Home Care Agencies About Getting Clients Online
Home care digital marketing requires live call handling, local search visibility, and separate lead pipelines for private-pay clients, Medicaid, and caregivers.
Shopify SEO Apps Compared: Structured Data Features
Compare four Shopify SEO apps on structured data alone: schema types, review support, Merchant Center, custom schema, languages, and pricing, so you can choose with confidence.
How to Validate Shopify Structured Data
Learn how to validate Shopify structured data with Google’s Rich Results Test, Schema Markup Validator, and Search Console to find and fix common schema errors step by step.
JSON-LD vs. Microdata: Differences for Shopify
Compare JSON-LD vs. Microdata for Shopify. Learn how each format works, which is easier to maintain, how they handle Product Schema, and how to validate your structured data.
Imagify for WordPress: Features, Pricing & a $6/Month Deal for 1,000 MB (2026)
Imagify for WordPress automatically compresses images, converts them to WebP/AVIF, and improves site speed with off-server optimization.
Is $10 a Day Enough for Google Ads? A Realistic Breakdown
A $10-a-day Google Ads budget works only when tightly targeted to local, low-CPC niches, while competitive industries require higher spend for data learning.
Filevine Case Management: Top Benefits for Growing Law Firms
Filevine case management software offers powerful AI tools and deep customization, making it ideal for high-volume personal injury and litigation firms.
Shopify Review Schema: Ratings and Structured Data
Learn how Shopify review schema works, how to add ratings and reviews to Product JSON-LD, validate markup, and fix common structured data issues.
SMBMarket Review 2026: Is It Worth $67/Mo for Business Buyers?
SMBMarket aggregates business-for-sale listings, deal tools, and coaching for $67 a month, serving as a consolidated platform for prospective business buyers.
How to Fix Missing validFrom in Merchant Listings
Learn how to fix missing validFrom errors in Google Merchant Listings, when the property is required, how to add it to Shopify JSON-LD, and how to validate the fix.
Shopify Product Schema vs. Google Merchant Listings
Shopify Product Schema vs. Google Merchant ListingsNEED HELP? CONTACT US 24/7 (877) 522-7738 Industries We Serve Law Firms & Legal Services Healthcare & Medical Practices Technology & SaaS Companies E-Commerce & Retail Home Service Finance Free...
Getting information about your case and your options is your FIRST move. Get a FREE case evaluation now…
Find Yourself a Marketing Expert Near You!
(877) 522-7738